AI your security team can review
We help your people use AI for business questions with permissions and query evidence their reviewers can examine. Databasin prepares the records and provides bounded investigation tools. Our team implements the application and its controls together, connecting the business result to the deployment your organization approves.
The application and its data path
We design how the application reaches its data as part of defining the work. The design identifies the records, their location, the model connection and the people allowed to use the result. Business and technical owners can assess those choices for the same use case.
The product can be hosted, installed in your Azure tenant or used alongside an existing platform. We configure the prepared views and connections for that deployment. Reviewers can follow a defined data route while the business team examines whether the application answers its question.
Controls we put into use
Governed views
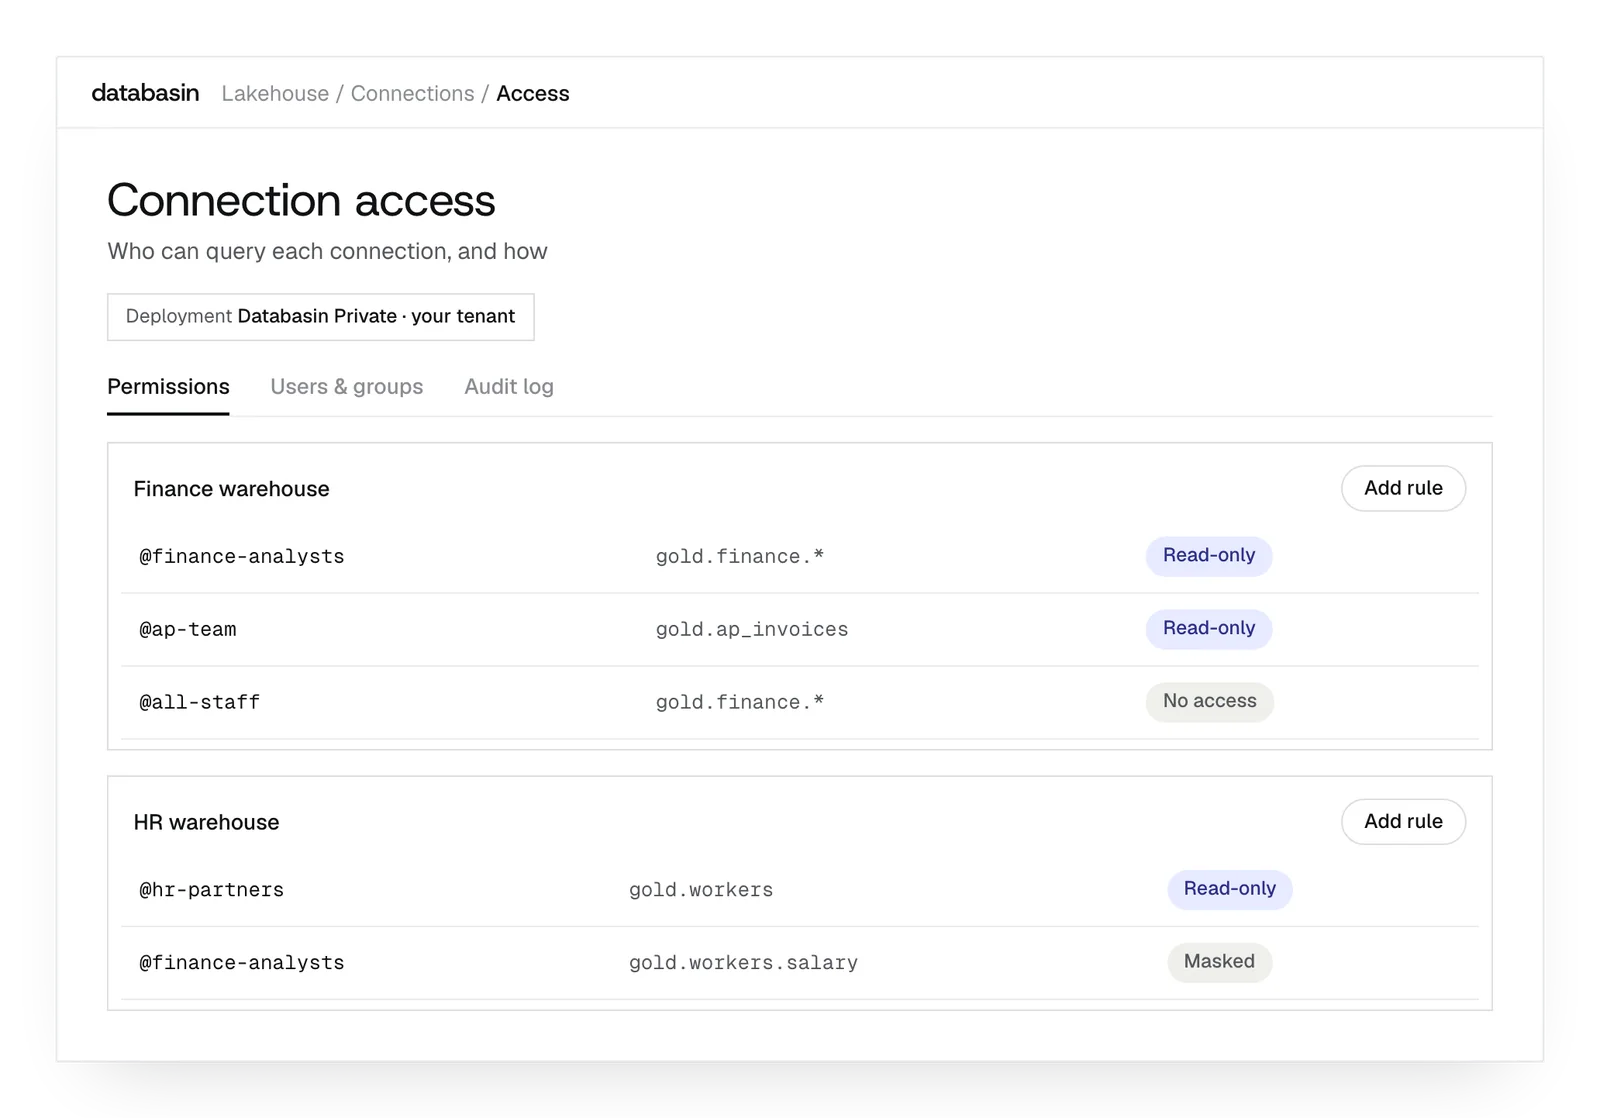
We implement prepared views and configure the permissions under which people can ask questions about them.
Bounded tools
We set query budgets, row caps and turn limits around the read-only tools an investigation can use.
Managed identities
We apply data access to the users and groups established for the organization and its selected deployment.
What can a reviewer inspect?
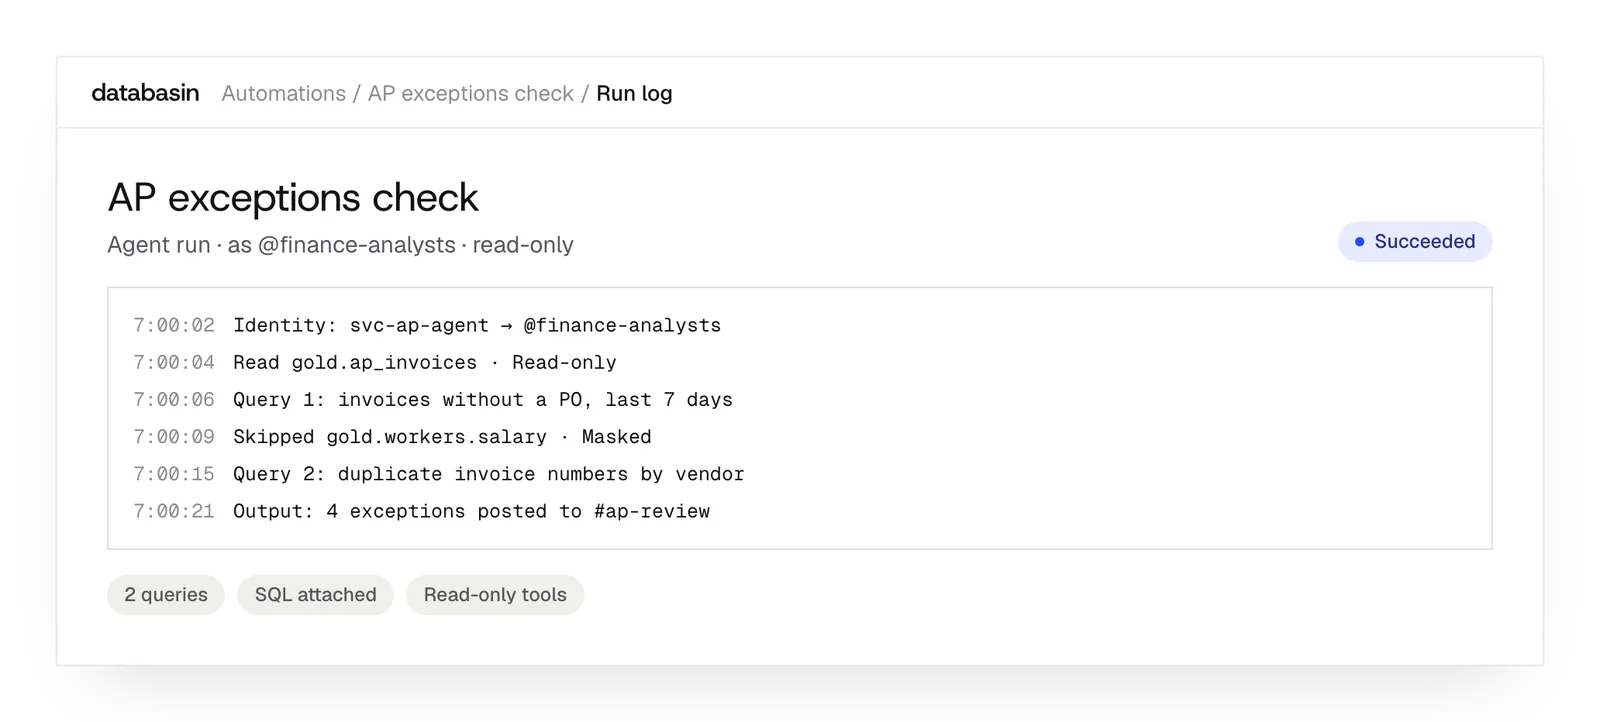
Reviewers can open the SQL returned with an answer and examine the calculation. For an agent, the run record also shows what it read and queried and the output it produced.
Our team can work through that evidence with the reviewers. Source permissions and the model connection are part of explaining how the investigation reached its result.
What happens next
We would like to hear where your team wants to make progress with data and AI. We can discuss a project you have in mind or explore where Databasin could help with the work.
What happens next
Book a demo
Book a conversation about your organization and the work you want to improve. Questions about where to start are welcome.
Explore the opportunity
We show a working example that answers your business questions, then discuss what it would take to deliver it for your team.
Get the first result
After agreeing the first use case, we implement it with your team. We train the people using it and measure how it performs.
FAQ
Who holds the infrastructure in a private deployment?
The Azure subscription, storage account, keys and virtual networks are yours. We implement Databasin Private within that boundary and describe the source and model routes needed by the application.
Can a security review consider the hosted service?
Yes. Databasin operates the hosted infrastructure. We discuss the records and access the application needs, and your organization evaluates whether the hosted mode fits its data and operating requirements.
Can the application use our existing data platform?
Yes. Databasin can work alongside Fabric, Databricks or Snowflake. The design sets out the prepared records, query route and permissions used by the application in that environment.
Can we use a model our organization has approved?
Yes. We can use an internally approved model. We discuss its endpoint and provider path with the reviewers so the route taken by data during an AI task is explicit.
Can an investigation agent update a production source?
No. Agent tools can read schema, run SELECT and fetch results. Writing, altering and deleting production-source data are outside those tools. Separately authorized automation operations use their own explicit permissions.
Can we limit how much an agent investigates?
Yes. The skill specifies its task, tools and run limits, including turns, queries and rows. Its access comes from the connection. The skill can restrict that access further but cannot expand it.
Does Sail support tables protected by row filters or column masks?
Sail currently refuses tables protected by row filters or column masks. We account for the required controls when selecting the query engine and route for the application.
Is a BAA available for work involving PHI?
Yes. A BAA is available and Databasin is HIPAA-ready. The review concerns the actual deployment, data flow, permissions and procedures. The trust center provides the choices and documents for that discussion.
Is a Databasin SOC 2 report available?
Databasin currently holds neither its own SOC 1 nor SOC 2 report. The trust center describes that position and the evidence available. We can discuss its controls and agreements with the proposed architecture.
Are project administration and data access the same permission?
They are separate. Project roles govern changes to configuration; connector governance controls which records a user can read. Someone can query permitted data without having permission to edit the pipelines.
Discuss the application and its controls
Talk with us about where the evaluation stands and what your teams want to understand. We can explore the intended business result and the deployment, data access and evidence needed to put it into use.